

Incident investigation is a Pro feature.
Requirements
- Each host needs a monitoring agent that is reporting. Hosts without one do not appear in the host pickers.
- Investigations use hosted AI. Each message you send uses one hosted prompt from your daily quota, even if the assistant is set to a custom endpoint. See AI assistant.
- For security evidence, turn on security event capture on the host.
Start an investigation
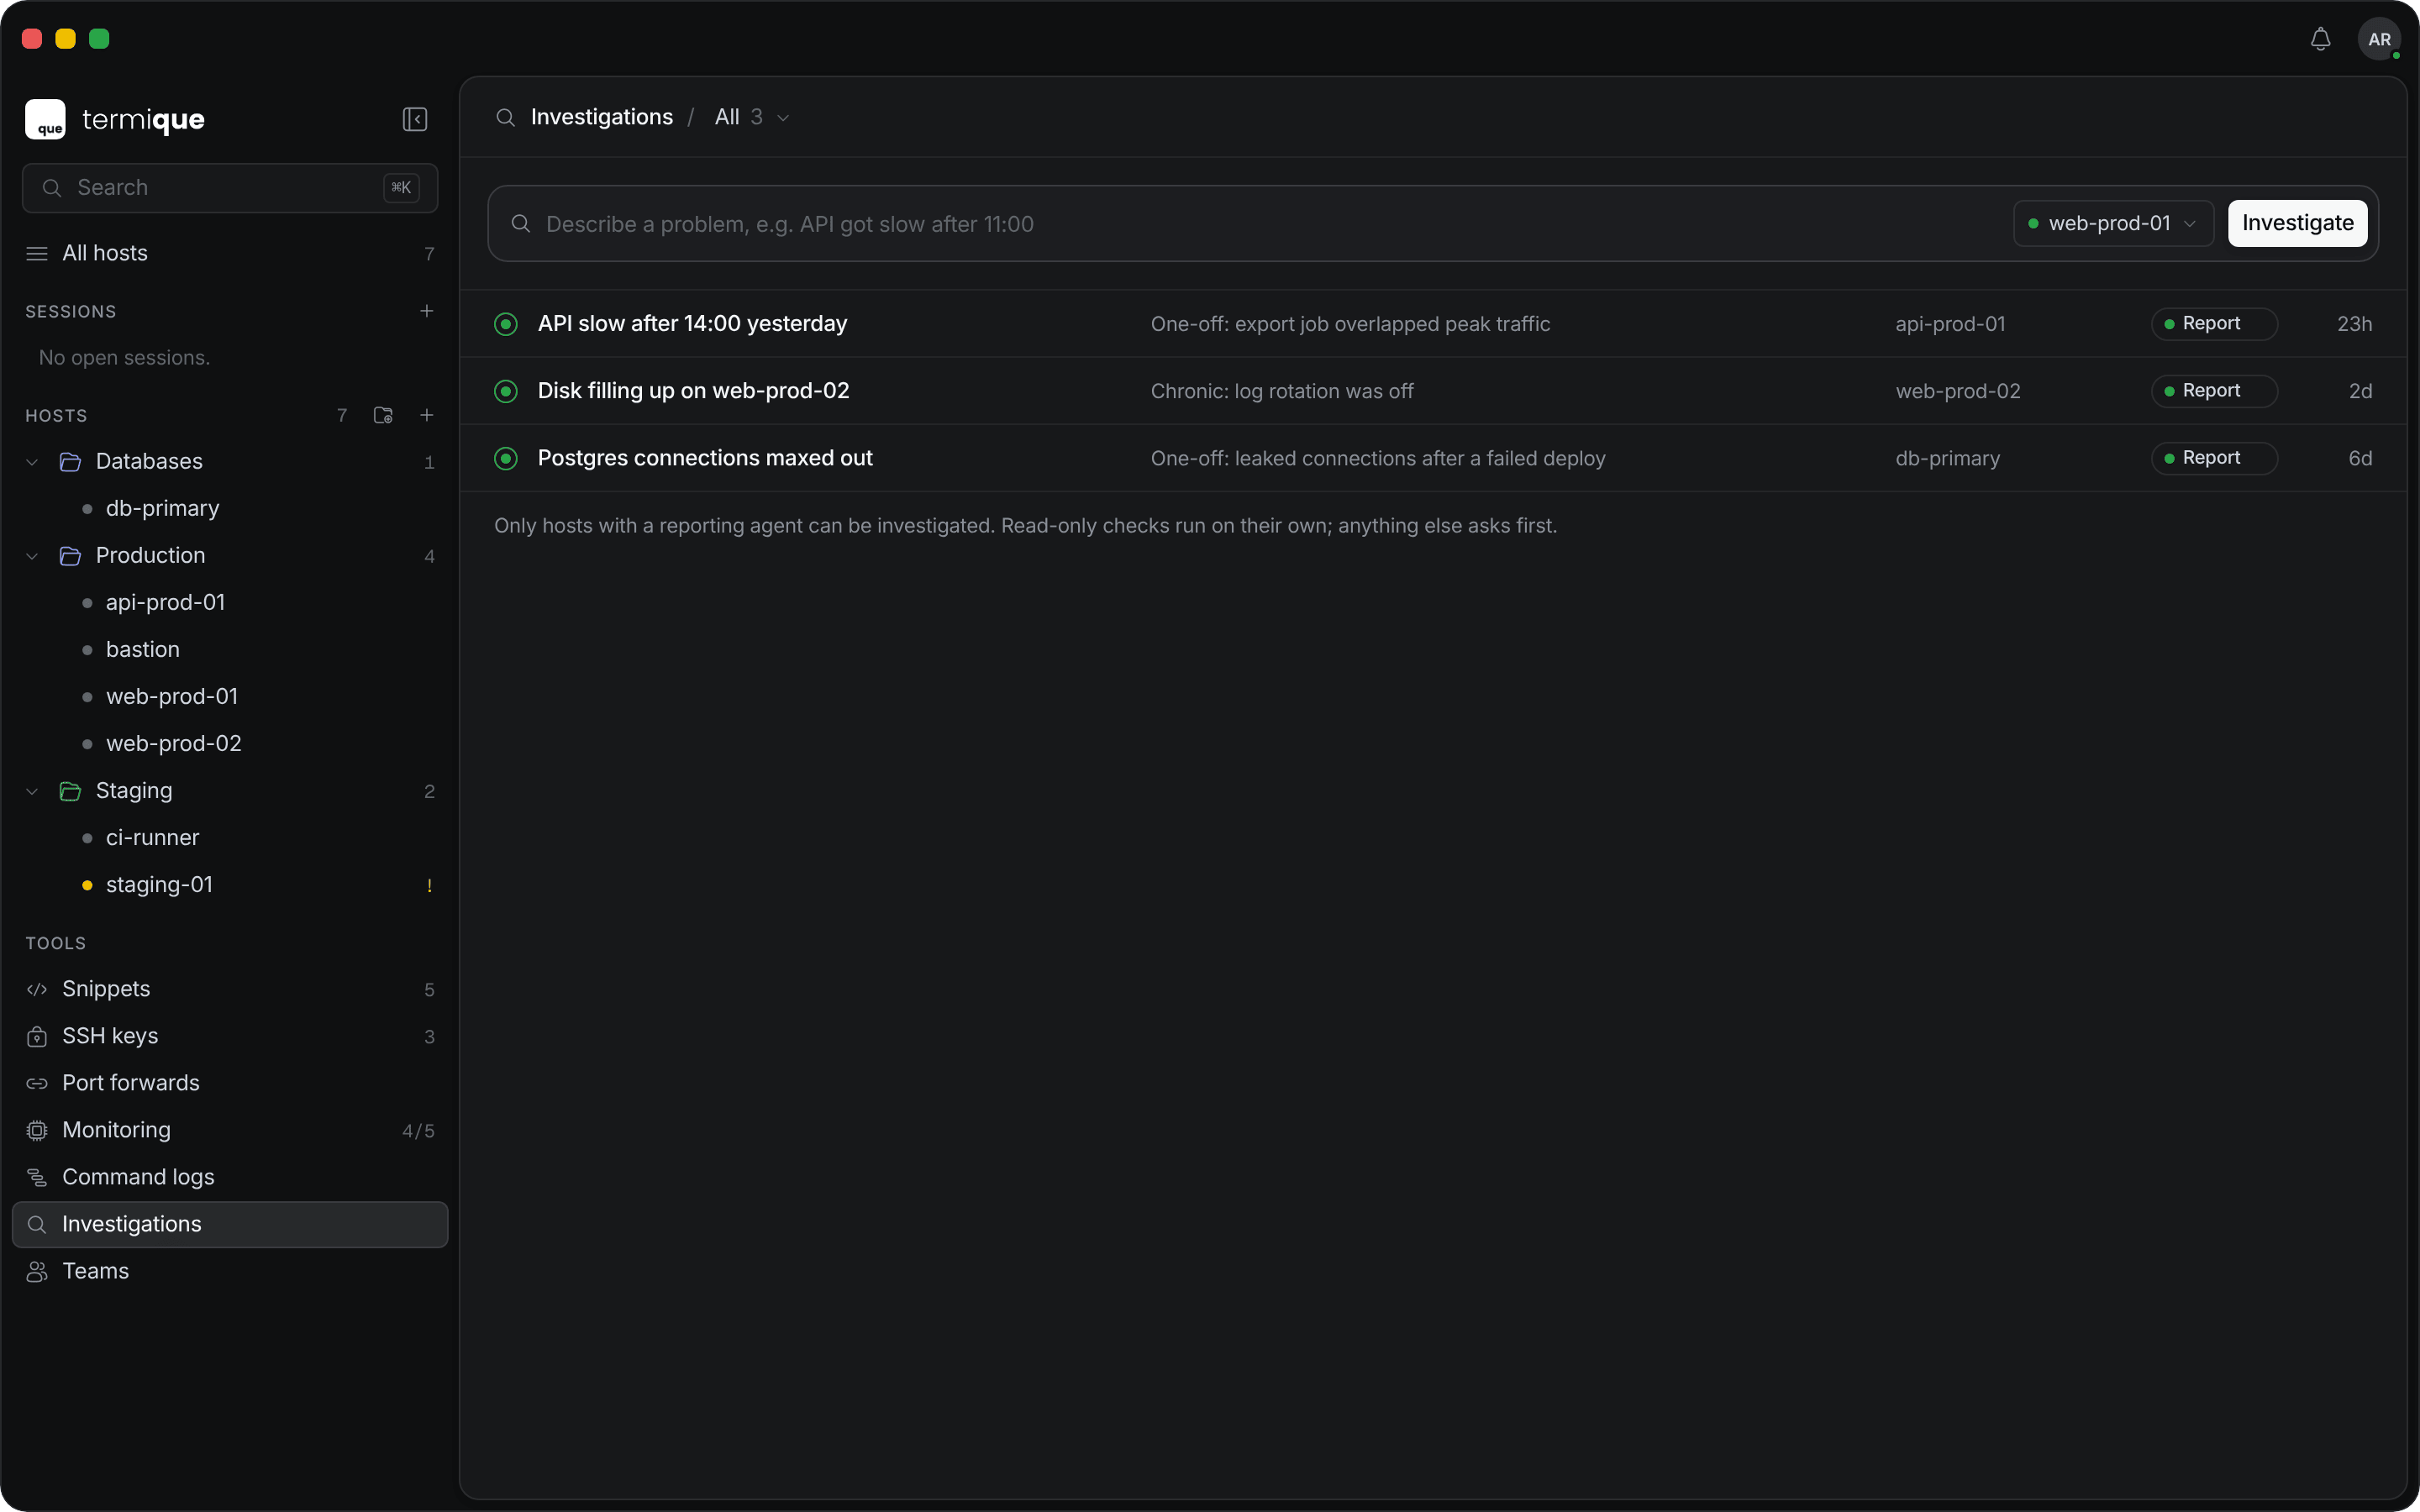
You can start an investigation from three places:- Investigations in the sidebar. Pick hosts with the host picker next to the search field, then click Investigate. The page also lists open investigations and past reports.
- A host’s detail page. Click Investigate this host in the side panel. It appears when the host’s agent is reporting.
- The Monitoring page. Click Generate report in the header, select a host and a Time window, and click Start investigation. The window you pick is preselected under When did it start?. 7 days opens as Pick a time, set to a week ago.
Describe the incident
A new investigation opens on What happened?- Under When did it start?, pick Last hour, Last 6 hours, Last 24 hours, or Pick a time to enter the start time.
- Pick a suggested prompt, or describe the incident in your own words, for example
API got slow after 11:00.
since <time>.
If you type a description on the Investigations page before clicking Investigate, the investigation starts right away with the last hour as its incident window. Leave the field empty to pick the window first.
How it works
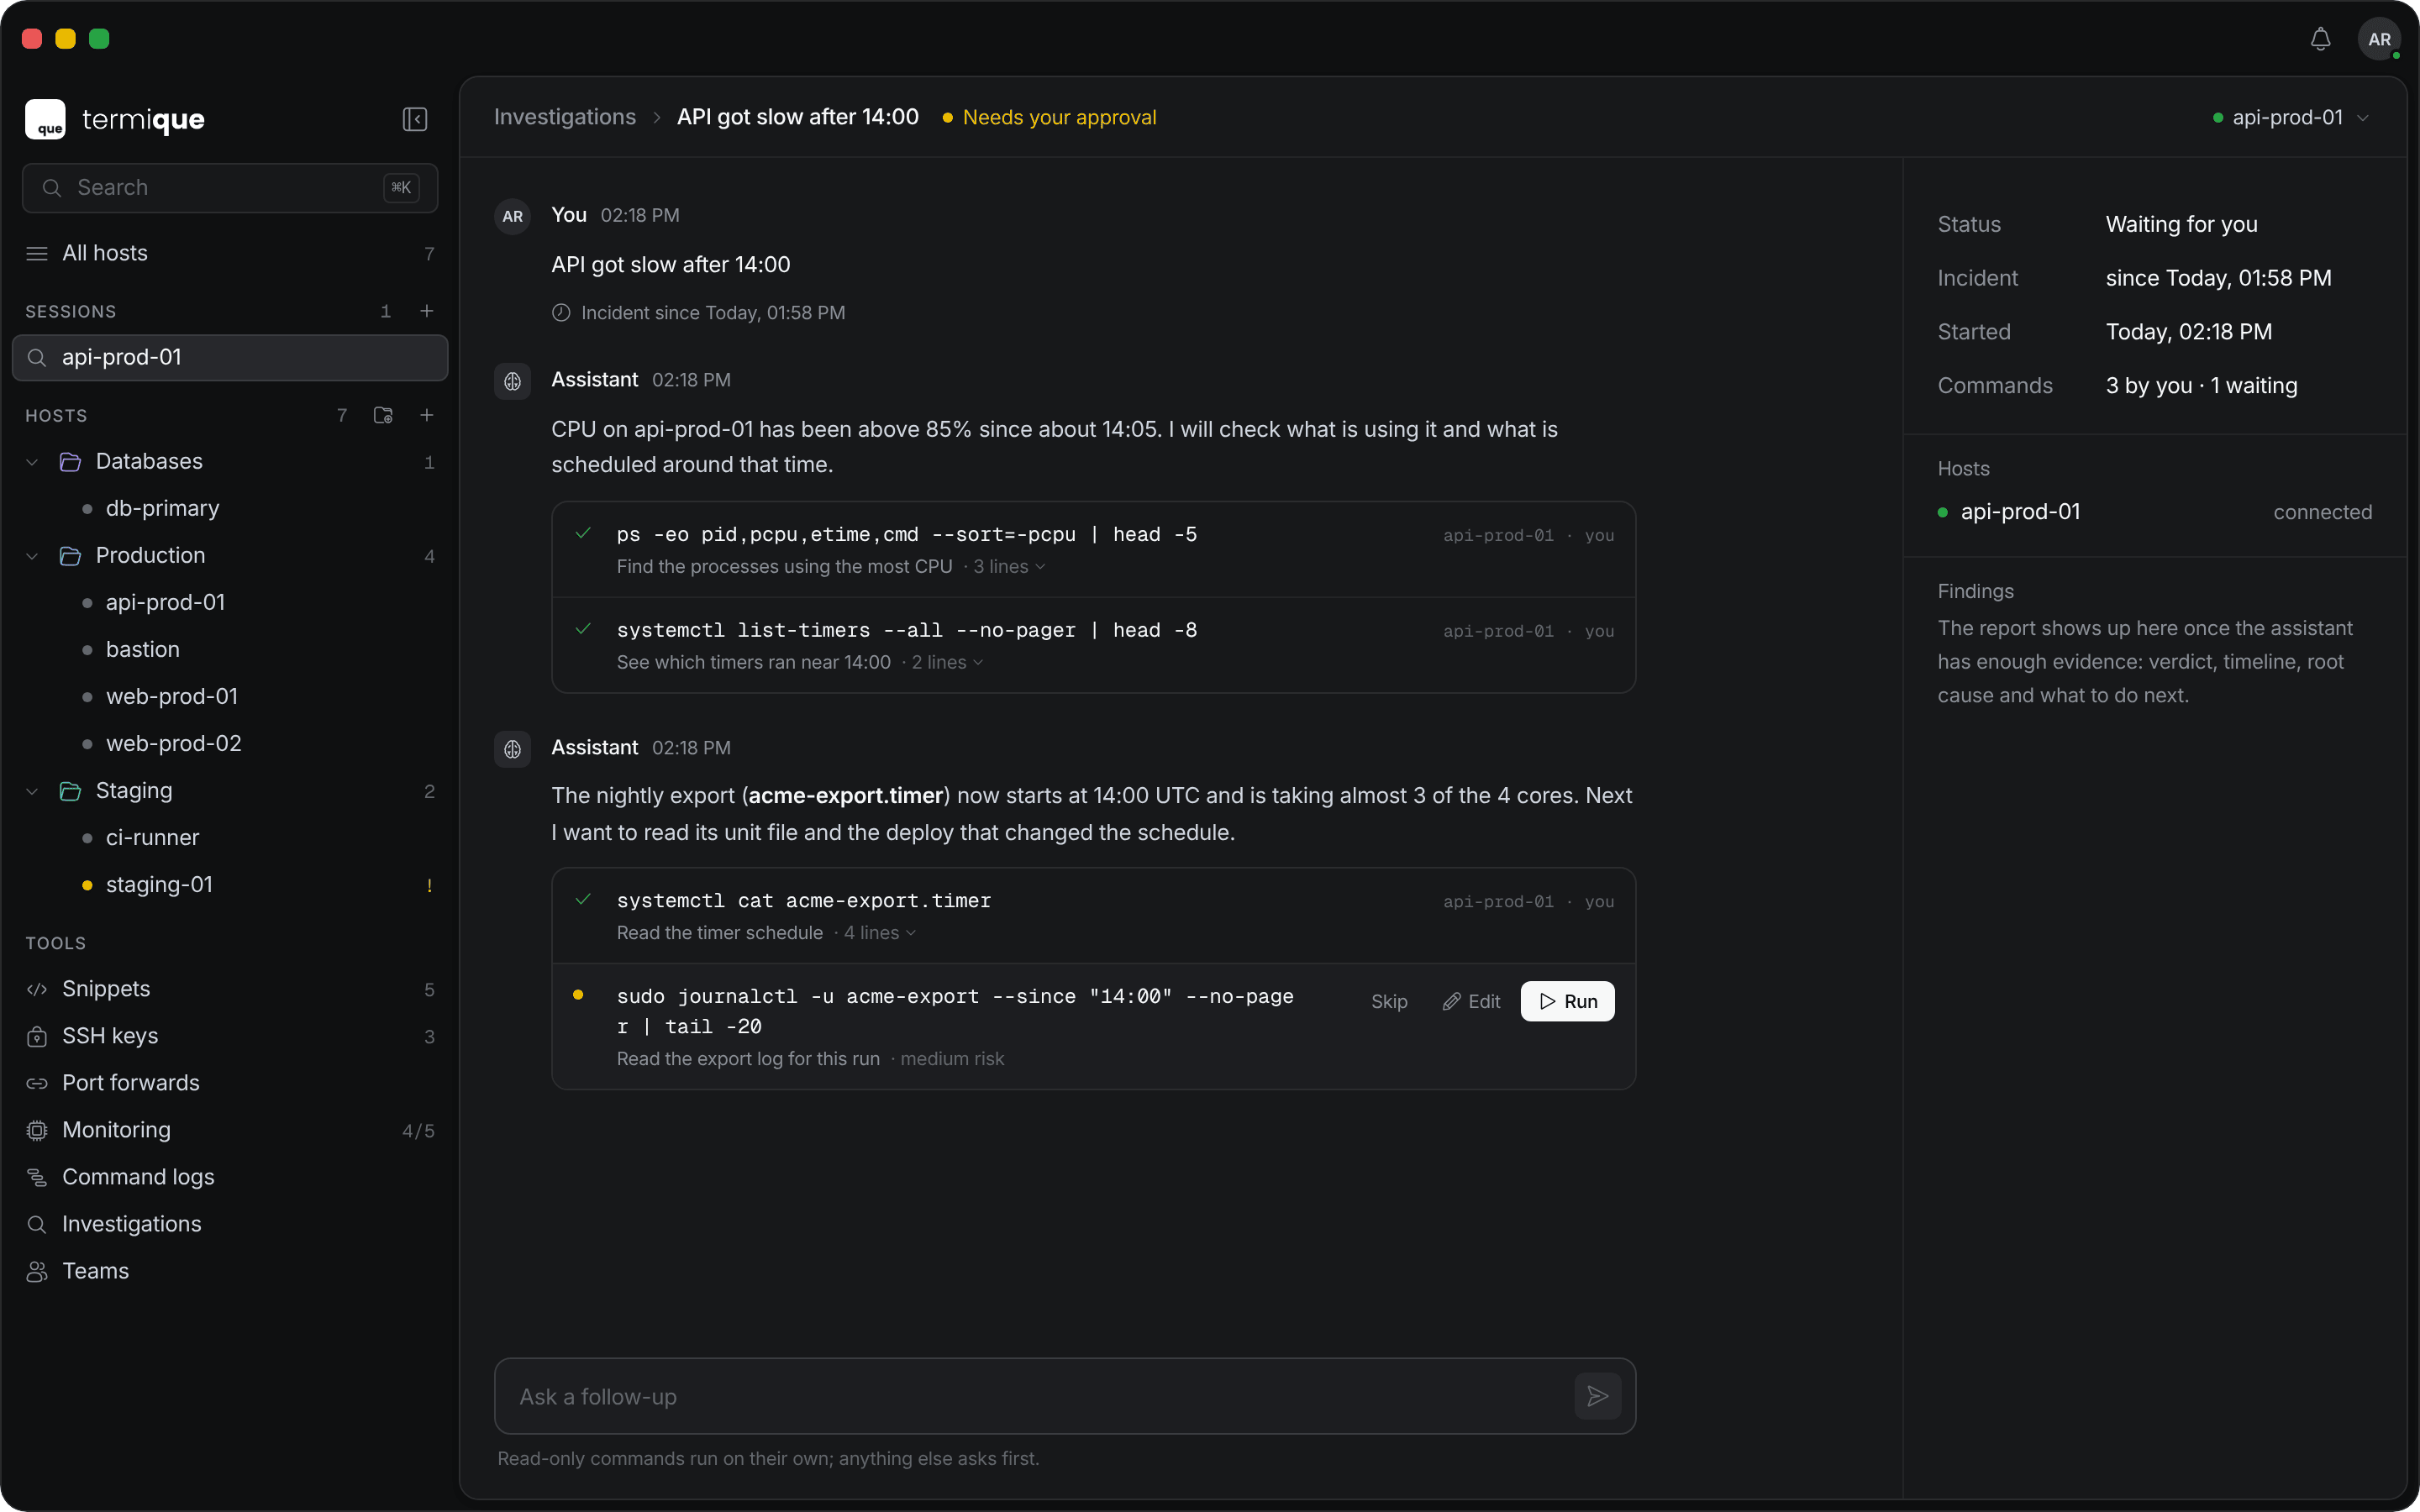
The assistant gathers evidence with:- Live commands on the selected hosts, over your open SSH sessions. If a host has no connected session, the investigation opens one.
- Monitoring history: CPU, memory, and disk from Monitoring, including ranges before the investigation started.
- Security events: SSH logins,
fail2banbans, and HTTP spikes and brute force, if capture is on for the host. One query covers up to 7 days.
- A dot shows the model’s risk label: low, medium, or high.
- A high risk command needs a second click on Confirm.
- A command that matches a destructive pattern is marked Flagged. Click Run anyway, then Confirm, to run it.
- If the assistant does not say which host a command is for, pick one under Run on.
Case file
The panel on the right tracks the investigation:- Status, such as Investigating, Waiting for you, or Report ready.
- Incident, Started, and Commands (how many ran automatically, ran by you, are waiting, or were skipped).
- Hosts, with each host’s connection state.
- Findings, a summary of the report once it exists.
The report
The assistant submits the report when it has enough evidence. To end early, click Finish with report. The assistant stops running commands and writes the report from what it has, calling out what it could not confirm. Click View report to open it: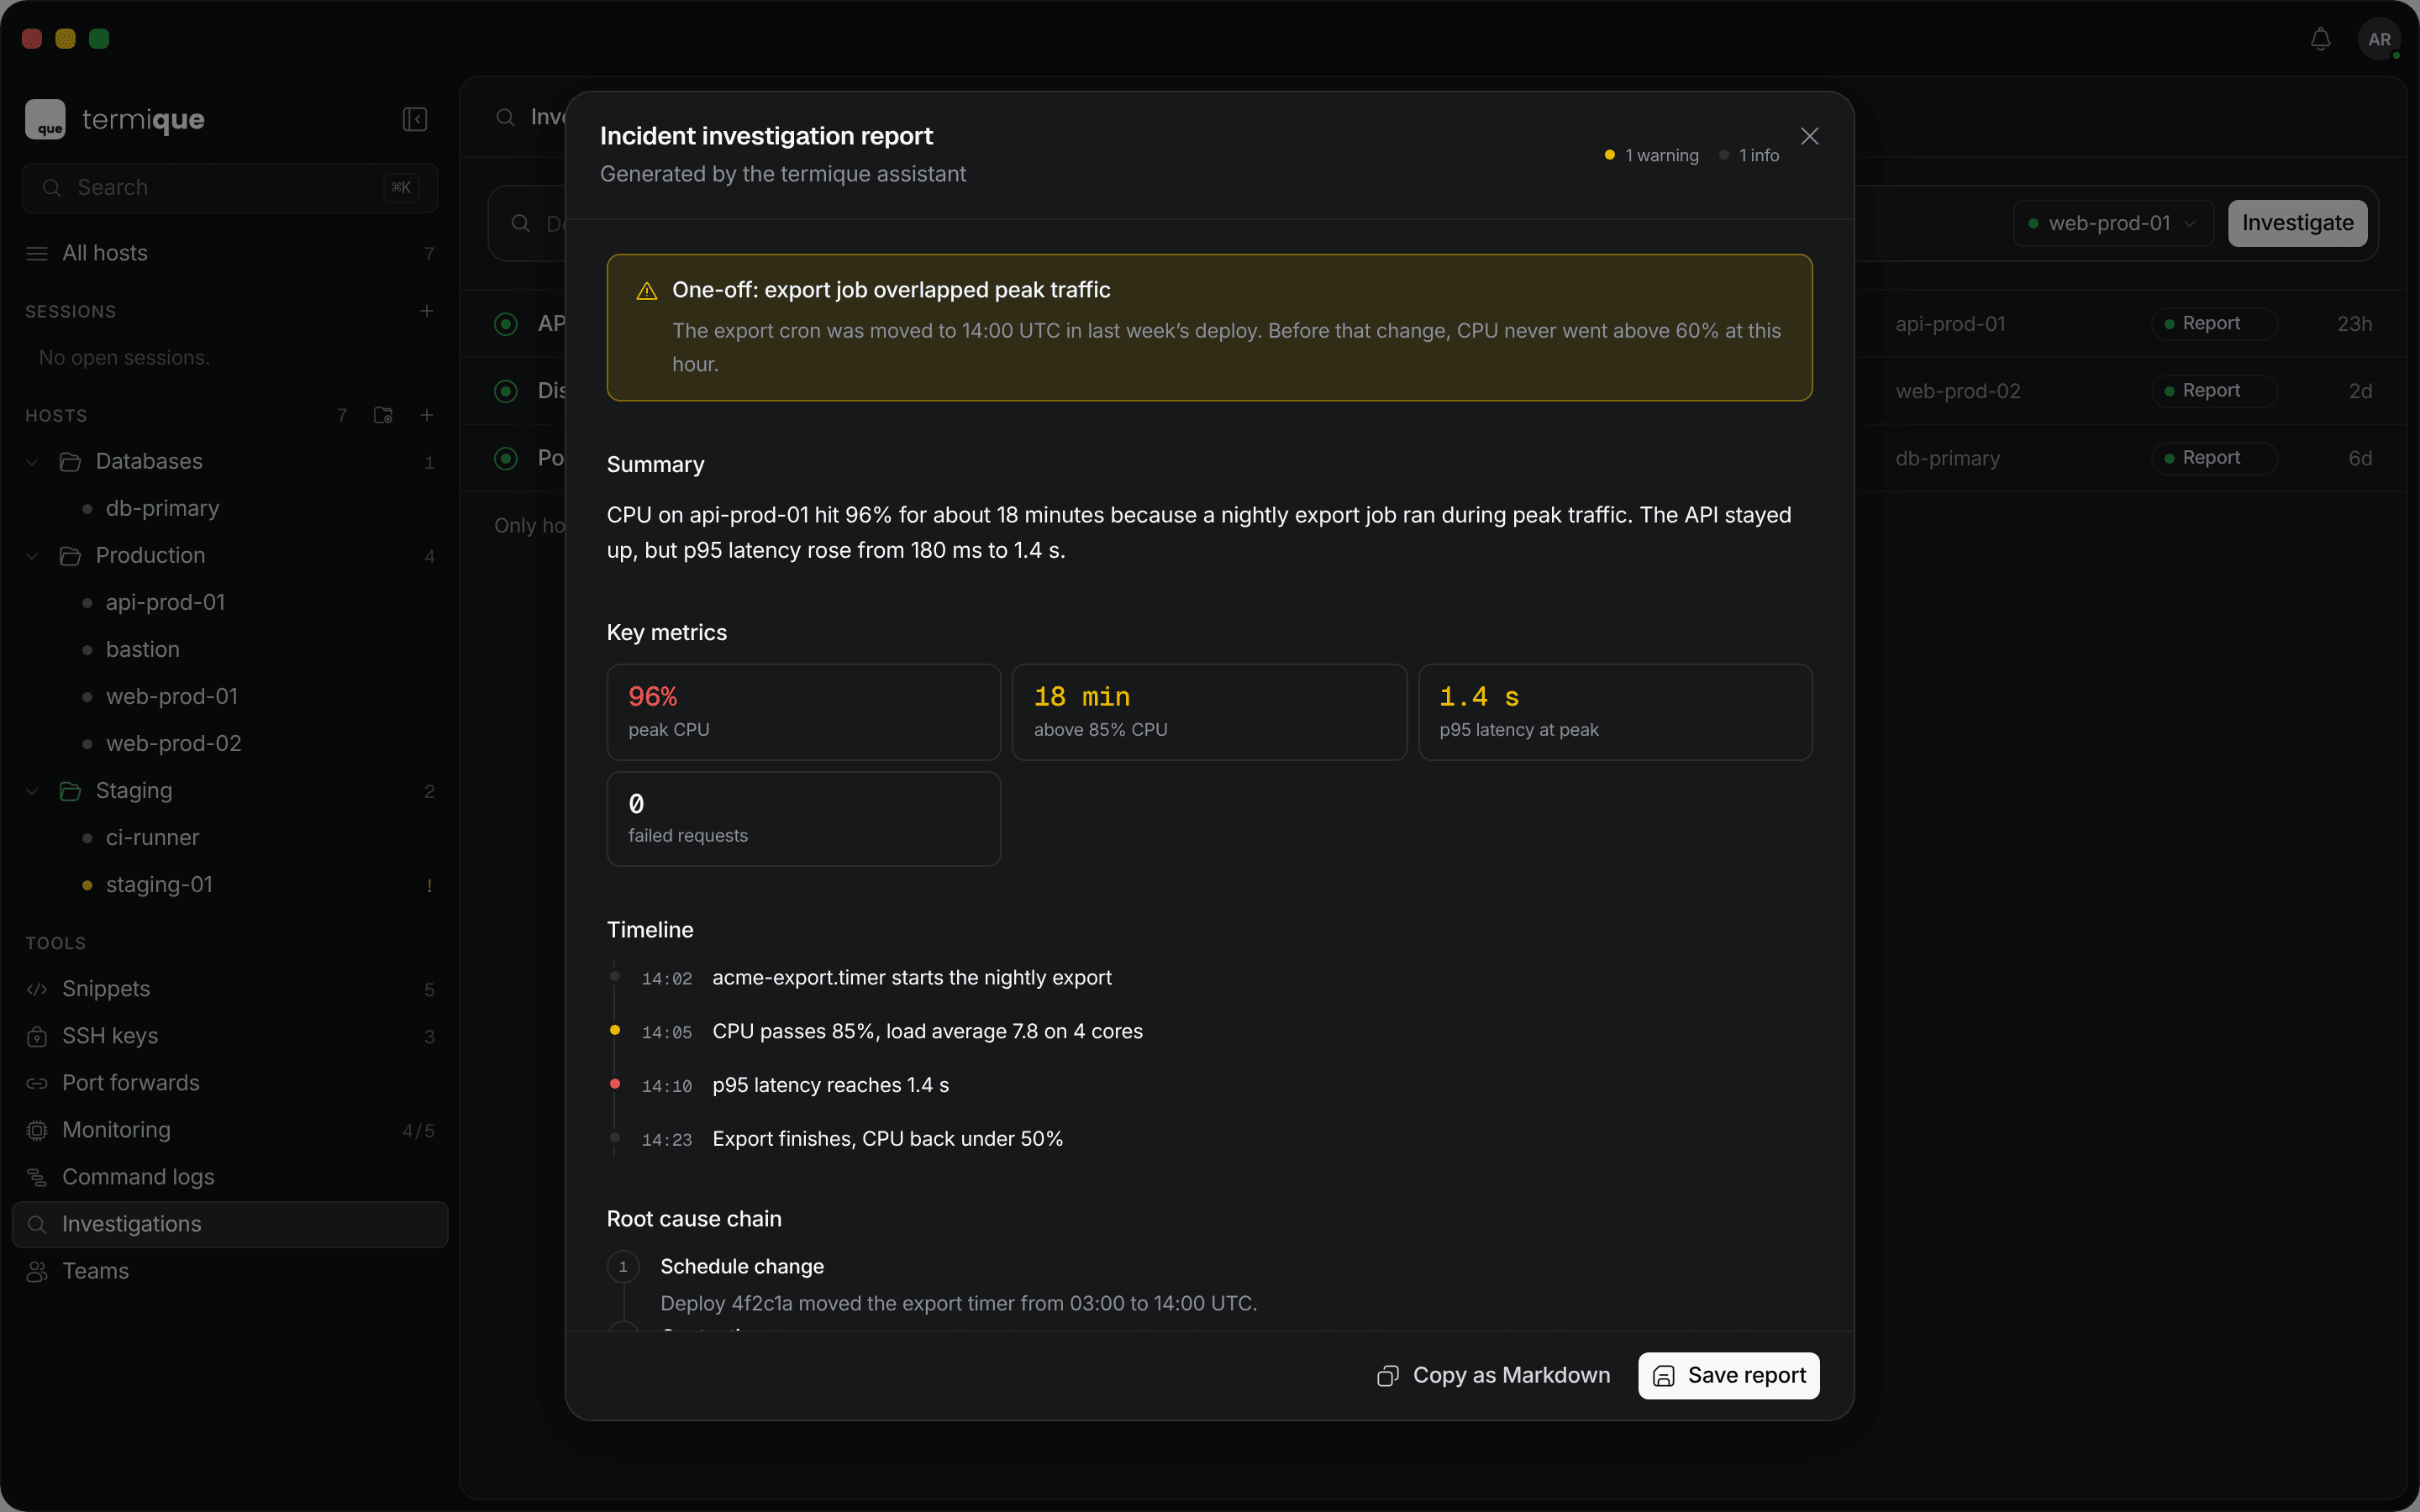
Evidence check
Termique cross-checks each finding against the command output and data the investigation collected. A finding shows one of:- Automated check matched a cited number to collected evidence
- Could not automatically match this claim to collected evidence
- No numeric claim to automatically check
Export
- Copy as Markdown copies the report to the clipboard.
- Save report saves it as an HTML file.