

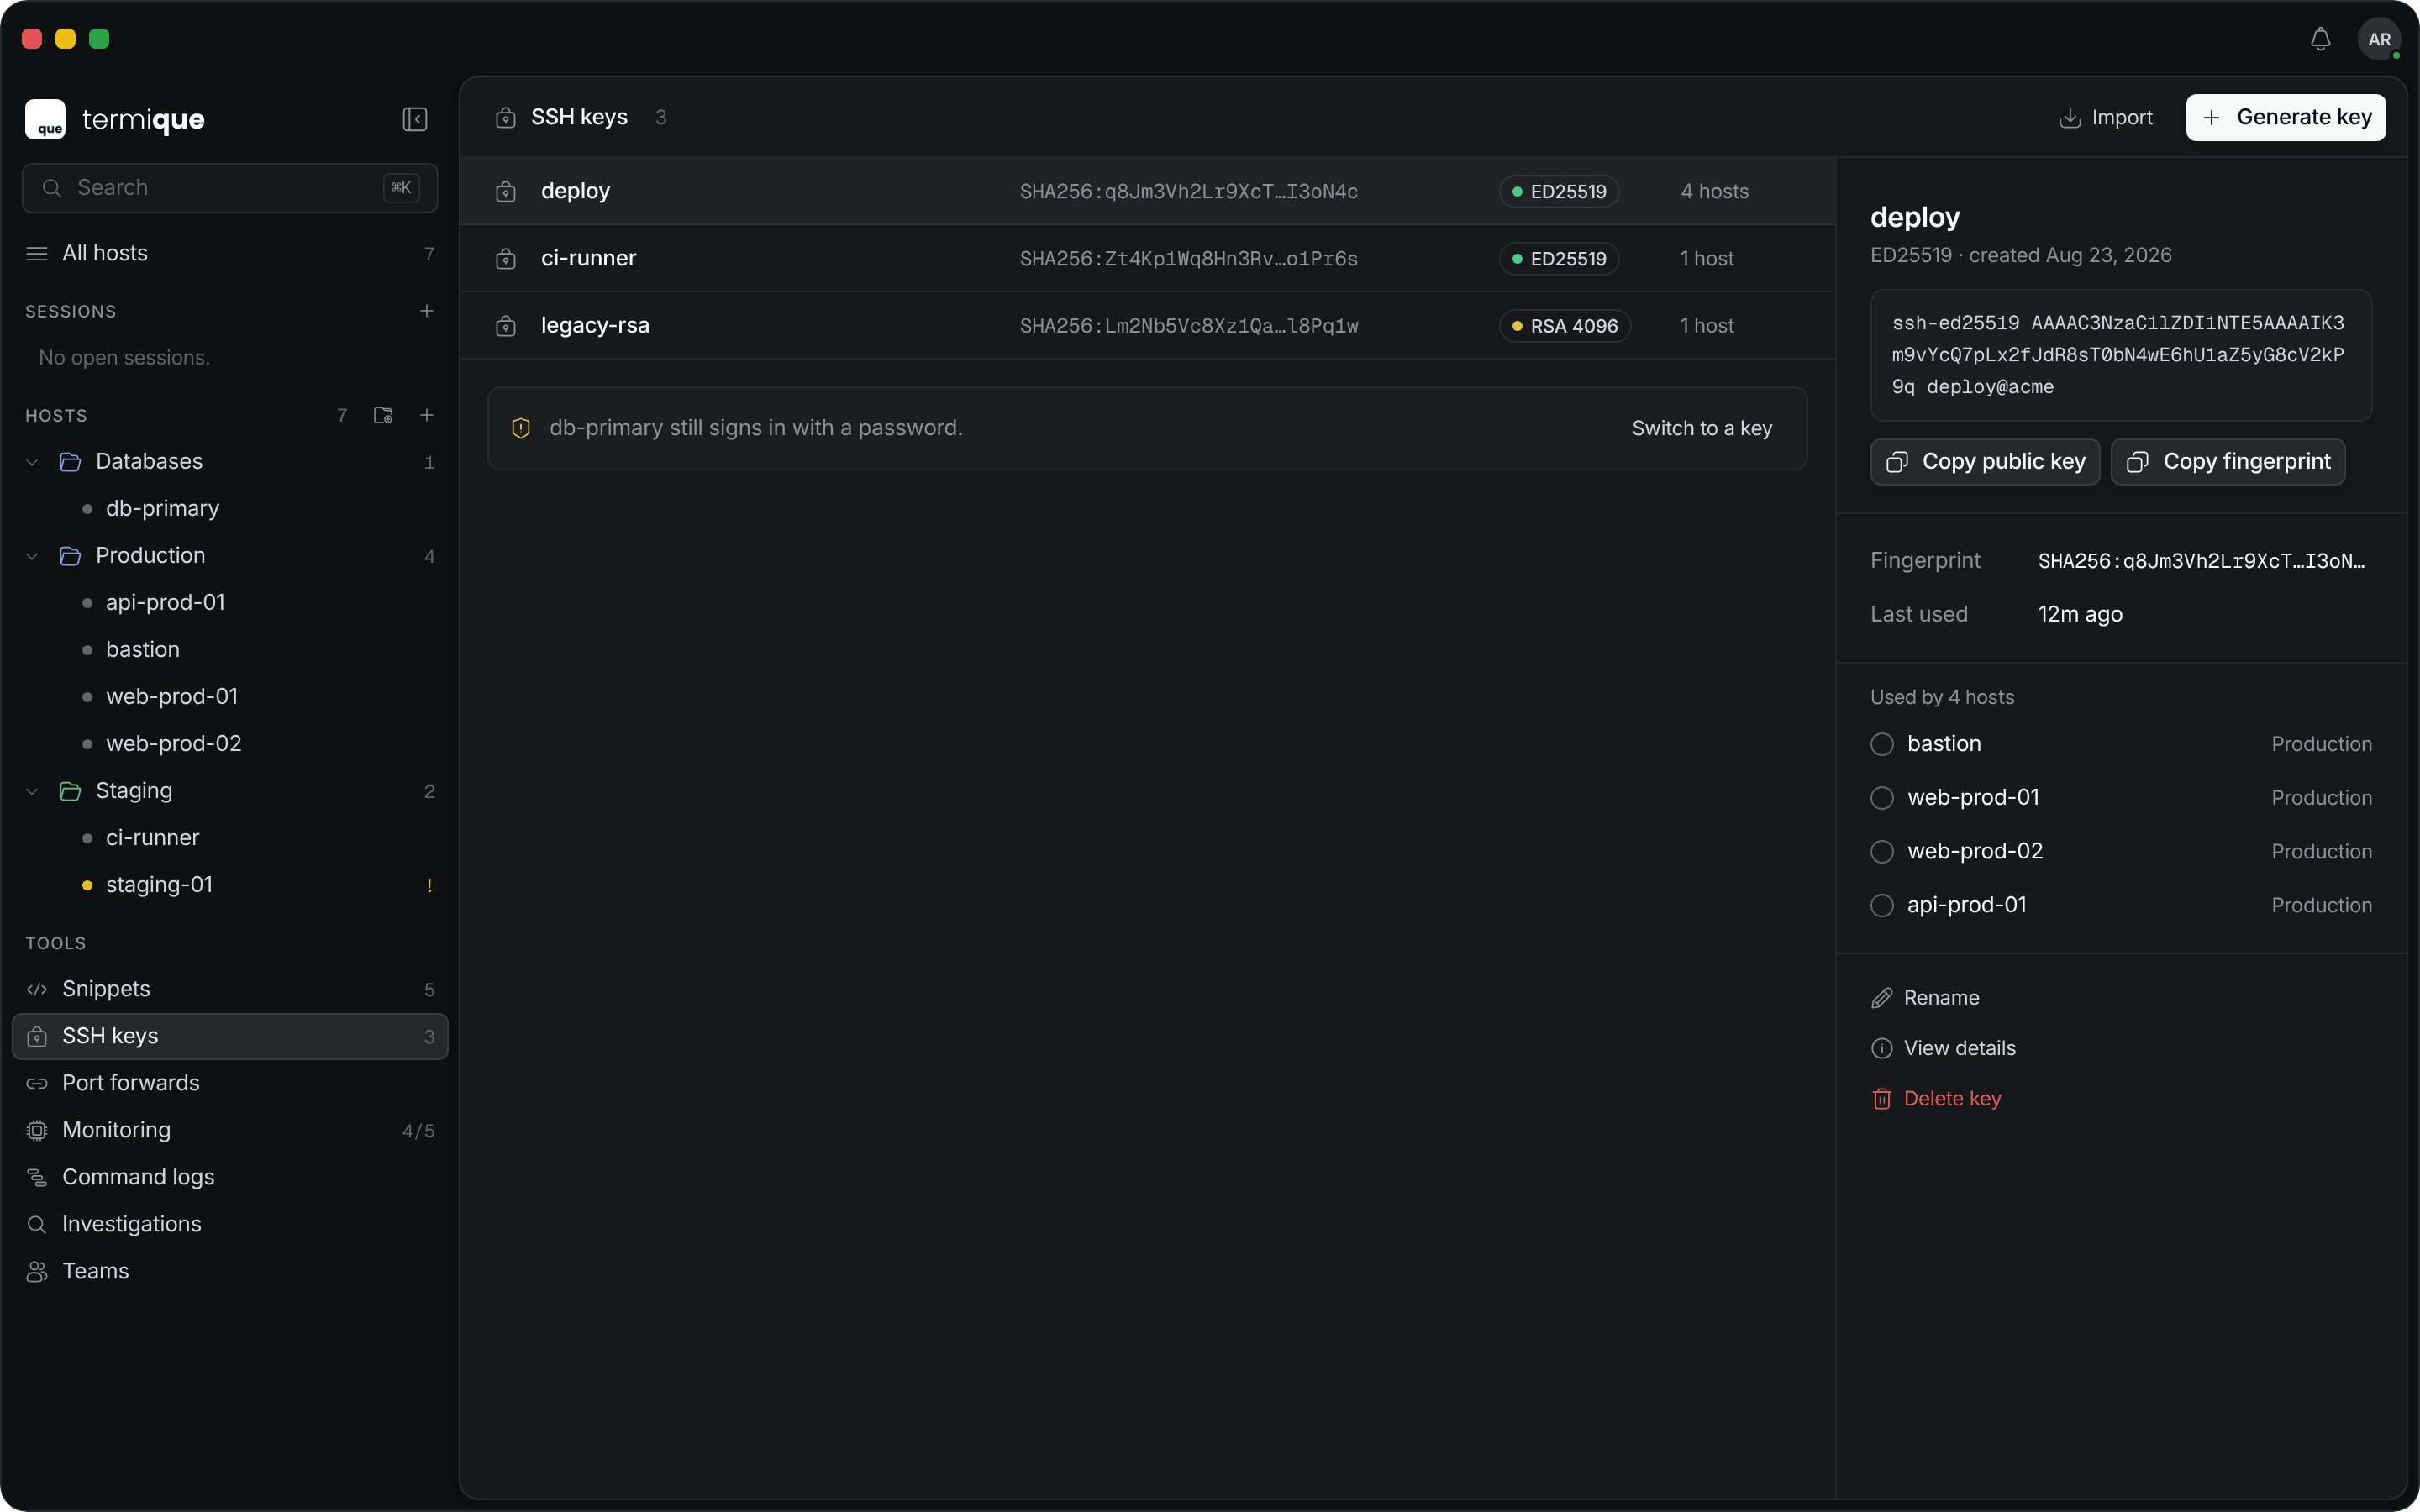
Generate a key
1
Open Generate SSH key
Click Generate key in the SSH keys header.
2
Name the key
Enter a Key name of at least 3 characters, e.g.
Work Laptop.3
Choose an algorithm
4
Generate
Click Generate key. The private key is encrypted with your DEK before it is stored or synced. Termique shows the Fingerprint and Public key.
5
Add the public key to your server
Click Copy public key and append it to
~/.ssh/authorized_keys on the server, or use Install on host. Click Done.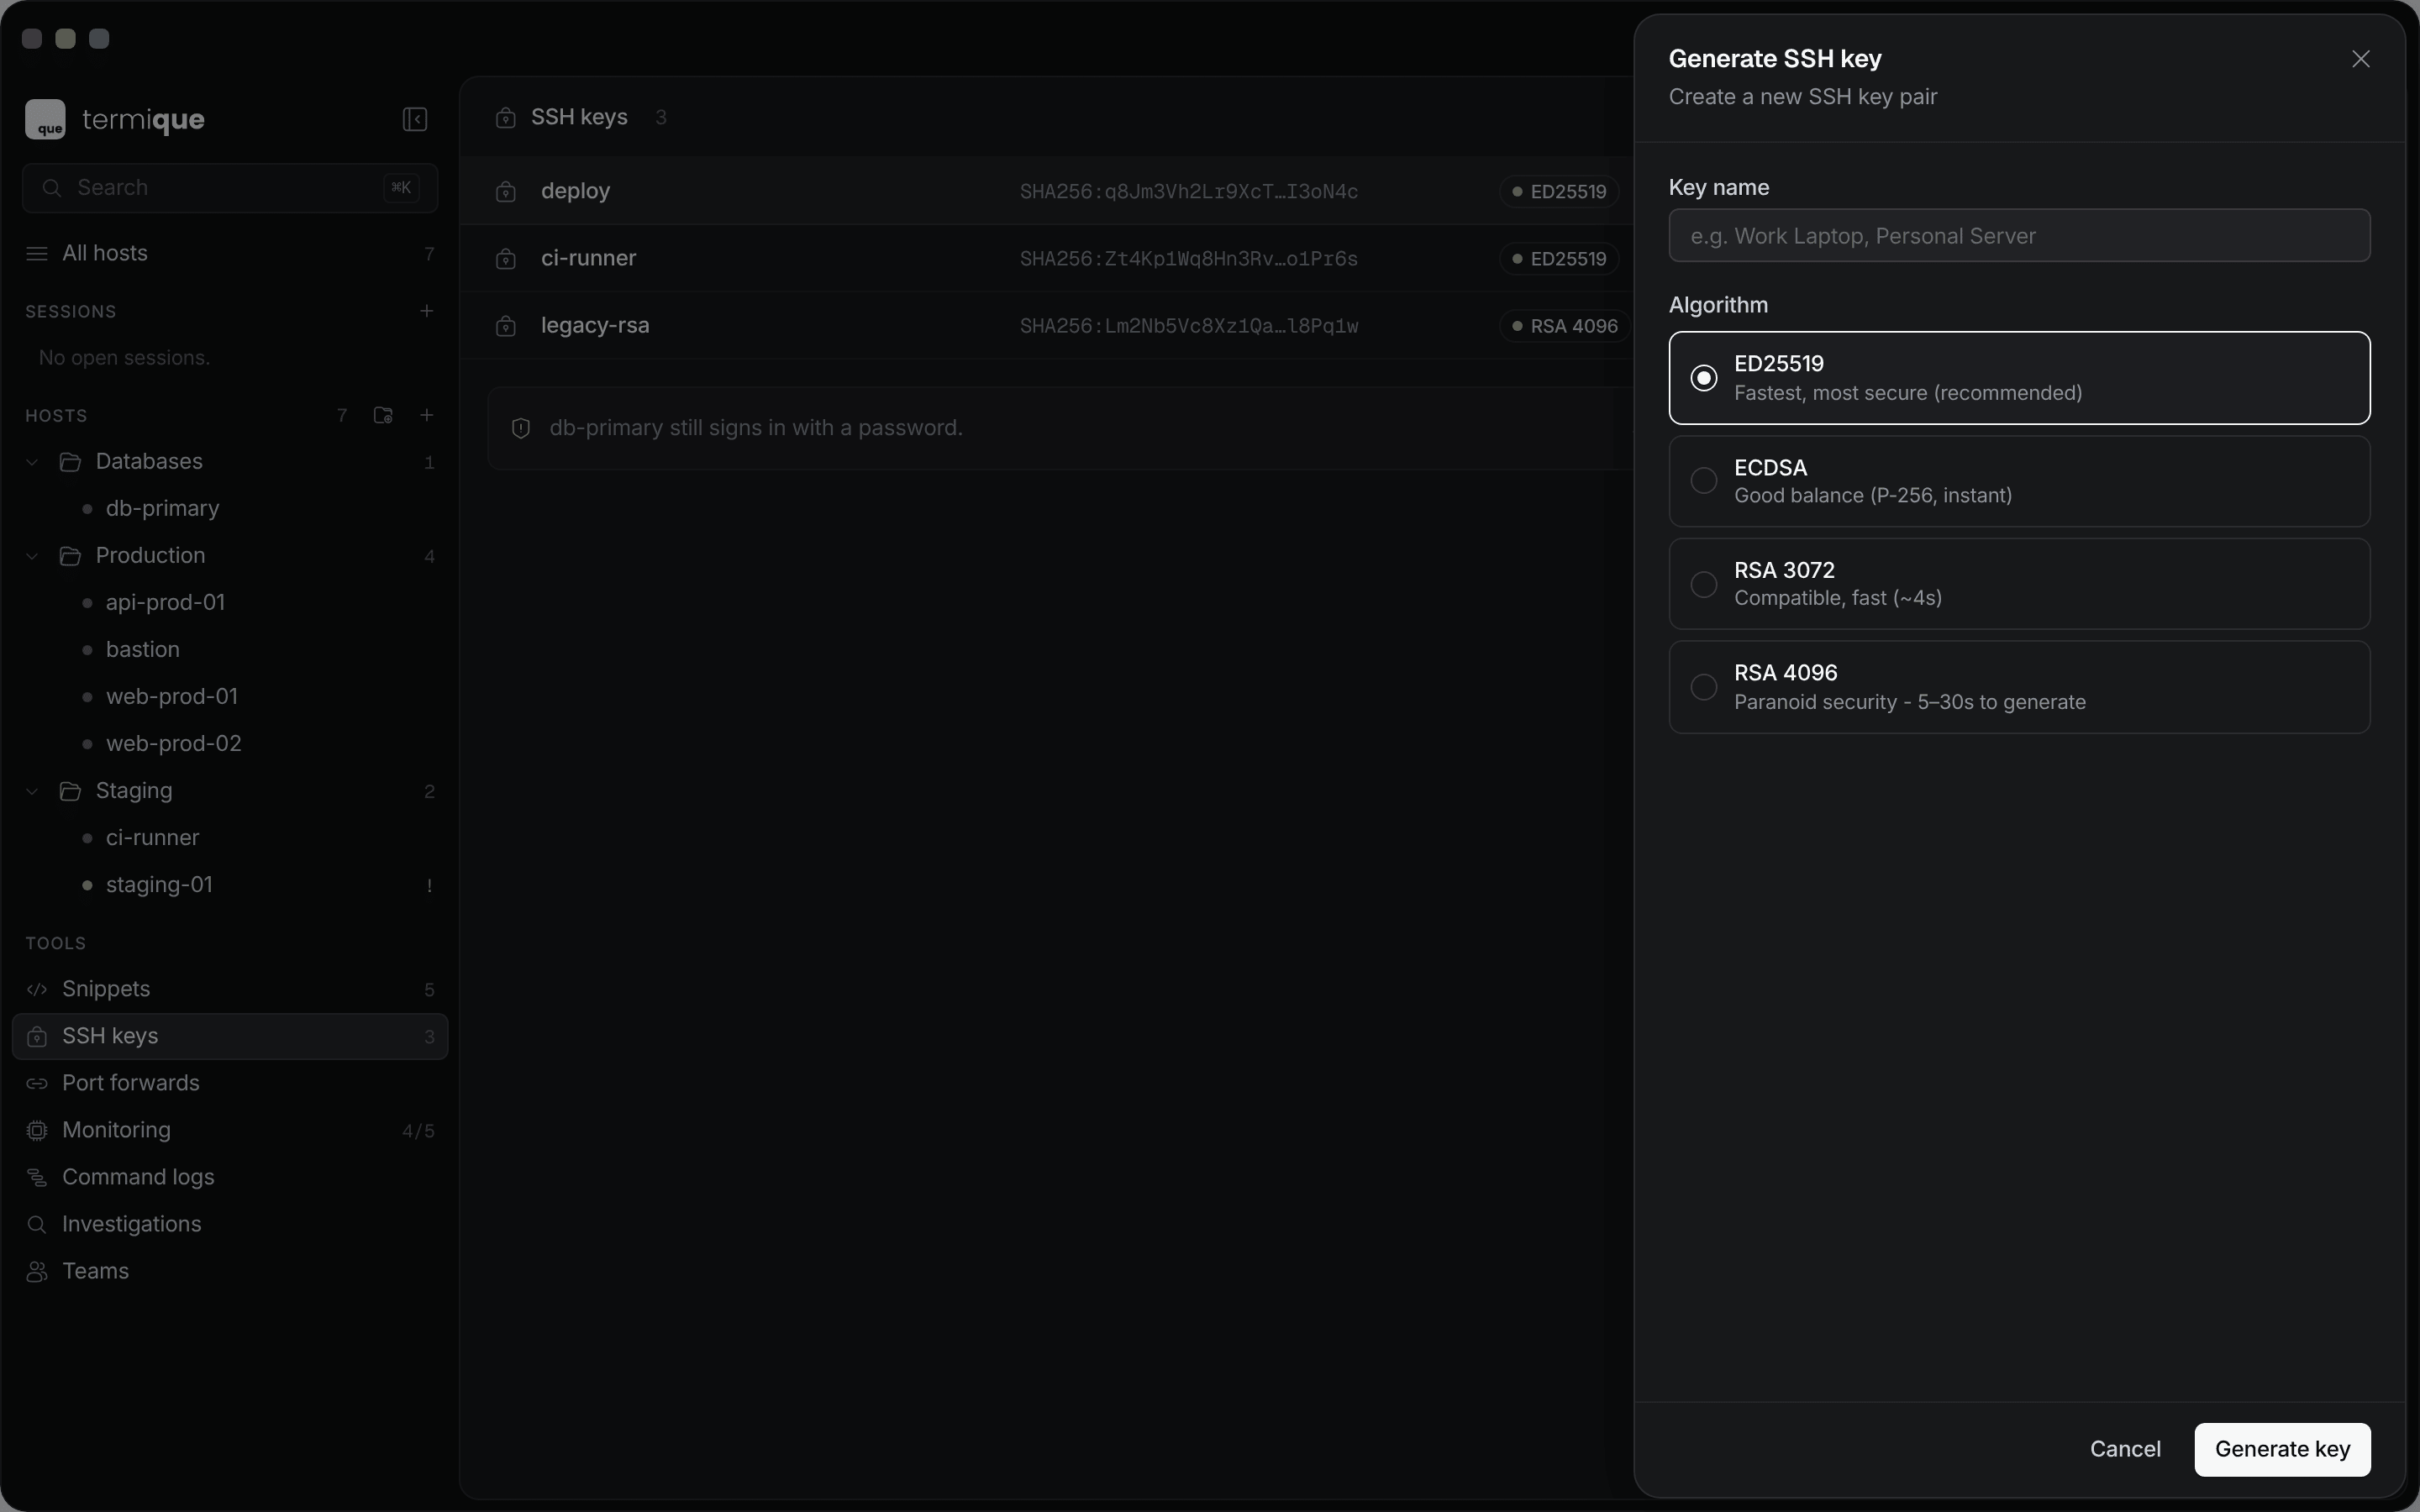
Import a key
1
Open Import SSH key
Click Import in the SSH keys header.
2
Add the private key
Enter a Key name, then paste the key into Private key or click Load from file. A key whose line breaks were lost in copying is reformatted automatically.
3
Enter the passphrase, if any
If the key is passphrase-protected, a Passphrase field appears. Termique checks the key, and the passphrase, as you type.
4
Import
When the sheet shows Valid … private key, click Import key.
Termique can only show the public key for keys in OpenSSH format. If Public key not available appears after an import, convert the key with
ssh-keygen -p -f <keyfile> and import it again.<label> key when you save the host. See Authentication.
Use a key for a host
When you add or edit a host, set Authentication to Stored SSH key and pick the key. See Hosts. If a key is passphrase-protected and Termique has no saved passphrase for it, connecting asks for it in Enter passphrase. Turn on Remember this passphrase to store it, encrypted with the key, and skip the prompt next time.Install a key on a host
Termique can append a public key to a server’s~/.ssh/authorized_keys over an open session.
1
Connect to the host
Open a session to the server, using its current password or another key.
2
Open the key's details
In SSH keys, select the key and click View details, or double-click it.
3
Install it
Under Install on host, pick the connected session and click Install.
~/.ssh and ~/.ssh/authorized_keys with the right permissions if they are missing, and adds the key only if it is not already there. Then edit the host and switch Authentication to Stored SSH key.
Key details
Select a key in the list to see it in the side panel:- The public key, with Copy public key and Copy fingerprint
- Fingerprint and Last used
- Used by: the hosts that authenticate with this key. Click a host to open it.
- Rename, View details, and Delete key
Verify a fingerprint
Fingerprints use the OpenSSHSHA256: format. To compare with a key on a server, run: